Updated 22 September 2026 · PET Group
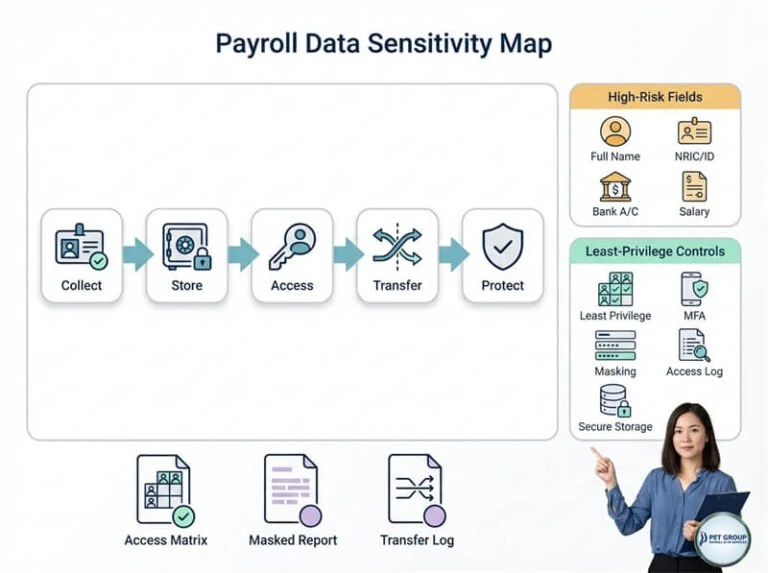
Map the information flow
Record where data comes from, who receives it and what each recipient needs. Separate employee-level processing access from management reporting. A manager who needs departmental costs may not need bank account details.
Controls to agree with your provider
- Named authorised contacts and an approved method of sharing files.
- Access by role and entity, with regular review and prompt removal when roles change.
- Verification of sensitive changes, especially bank details.
- Protected delivery of employee documents and a clear access-recovery process.
- Logging and escalation of accidental disclosure or suspected compromise.
- Retention, secure deletion and return-of-data arrangements when the service ends.
Regional data handling
Before Malaysia–Singapore transfers, identify the entities and systems involved and confirm the applicable safeguards. Singapore’s PDPC describes protection, retention and overseas-transfer obligations; Malaysian requirements must also be assessed for the relevant processing. This checklist is a starting point for that discussion, not a certification of compliance.
Questions to ask before go-live
Who can download payroll records? How is a misdirected file handled? What happens when an approver leaves? Who retains the final payroll evidence? Request clear answers and contractual responsibilities rather than relying on a generic statement that data is secure.
Official references
Check the current authority guidance when applying rules to an employee or payroll period. Sources reviewed on 22 September 2026.
See PET’s security approach and data protection policy.